DNS-over-HTTPS Setup Guide: Block ISP Tracking in 10 Minutes
Advertisements
Taking control of your online privacy starts with securing your web queries, and following a DNS-over-HTTPS Setup Guide is the fastest fix. Encrypting your domain requests prevents your internet service provider from logging every website you visit and building a detailed browsing profile.
By routing plain-text lookup traffic through an encrypted HTTPS tunnel, DoH shields your home network from third-party monitoring and data broker harvesting. Upgrading your resolver settings on desktop, mobile, and router configurations locks down personal activity without sacrificing browsing speed.
Hardening your connection takes less time than a coffee break and requires zero specialized networking software. Let's walk through the simple configuration steps to block ISP tracking and secure all your personal devices in under 10 minutes.
Understanding the Imperative for DNS-over-HTTPS
In today's interconnected world, your online activities generate a digital trail, much of which can be observed by your Internet Service Provider. This data, known as DNS queries, reveals every website you visit, every app you use, and every service you access online.
ISPs can collect, analyze, and even sell this valuable browsing history to third-party advertisers or data brokers, often without your explicit consent. This practice raises significant privacy concerns for individuals and households alike.
Implementing a DNS-over-HTTPS setup guide is not merely a technical tweak; it is a fundamental step towards reasserting control over your personal data. By encrypting your DNS queries, you obscure this critical information from your ISP, drastically reducing their ability to track your online behavior.
What is DNS-over-HTTPS (DoH) and How Does it Work?
DNS-over-HTTPS (DoH) is a protocol that encrypts DNS (Domain Name System) queries using the HTTPS protocol, the same encryption used for secure websites. Traditionally, DNS queries are sent in plain text, making them susceptible to eavesdropping and manipulation.
When you type a website address, like 'example.com', into your browser, your computer sends a DNS query to translate that human-readable address into an IP address that computers understand. Without DoH, this query is unencrypted, like sending a postcard through the mail.
With DoH, this query is encapsulated within an encrypted HTTPS connection to a DoH-enabled DNS resolver. This means your ISP can see you are connecting to a DoH server, but they cannot see the specific websites or services you are querying, effectively blocking their ability to track your individual browsing habits.
The Technical Underpinnings of DoH
Encryption Standard: DoH leverages TLS (Transport Layer Security) to encrypt DNS traffic, ensuring confidentiality and integrity.
Port Usage: Unlike traditional DNS which uses port 53, DoH utilizes port 443, the standard port for HTTPS, making it harder to block or differentiate from regular web traffic.
Privacy Enhancement: By obscuring DNS queries, DoH prevents ISPs and other intermediaries from logging your browsing history.
Key Benefits of DoH Implementation
Enhanced Privacy: Significantly reduces the amount of data your ISP can collect about your online activities.
Improved Security: Protects against DNS-based attacks such as spoofing and man-in-the-middle attacks.
Bypassing Censorship: In some regions, DoH can help bypass DNS-based censorship by routing queries through encrypted channels.
Preparing for Your DNS-over-HTTPS Setup Guide
Before diving into the technical configurations, it's crucial to understand the components involved and choose a reliable DoH provider. This preparatory phase ensures a smooth and effective implementation of your DNS-over-HTTPS setup guide.
A well-informed choice of DoH provider is paramount, as this entity will handle your encrypted DNS queries. Factors like privacy policies, performance, and additional security features should guide your decision.
Additionally, familiarizing yourself with your router's interface and device settings will streamline the setup process. This groundwork saves time and prevents potential complications during configuration.
Choosing a Reputable DoH Provider
Cloudflare (1.1.1.1): Known for speed and privacy, offering a strong commitment to not logging user IP addresses or selling data.
Google Public DNS (8.8.8.8): A widely used and reliable service, though some users might have privacy concerns regarding Google's data practices.
Quad9 (9.9.9.9): Focuses on security by blocking malicious domains and providing a privacy-first approach.
Gathering Necessary Information
Router Login Credentials: Essential for accessing your router's administration panel to modify DNS settings.
Device Operating System Details: Knowing your OS (Windows, macOS, Android, iOS) helps in finding specific DoH configuration steps for individual devices.
Preferred DoH Server IP Addresses: Note down the primary and secondary IP addresses of your chosen DoH provider.
Step-by-Step DNS-over-HTTPS Setup Guide on Your Router
Configuring DoH at the router level is the most effective way to protect all devices connected to your home network simultaneously. This centralized approach ensures consistent privacy across all your smart devices, computers, and mobile phones.
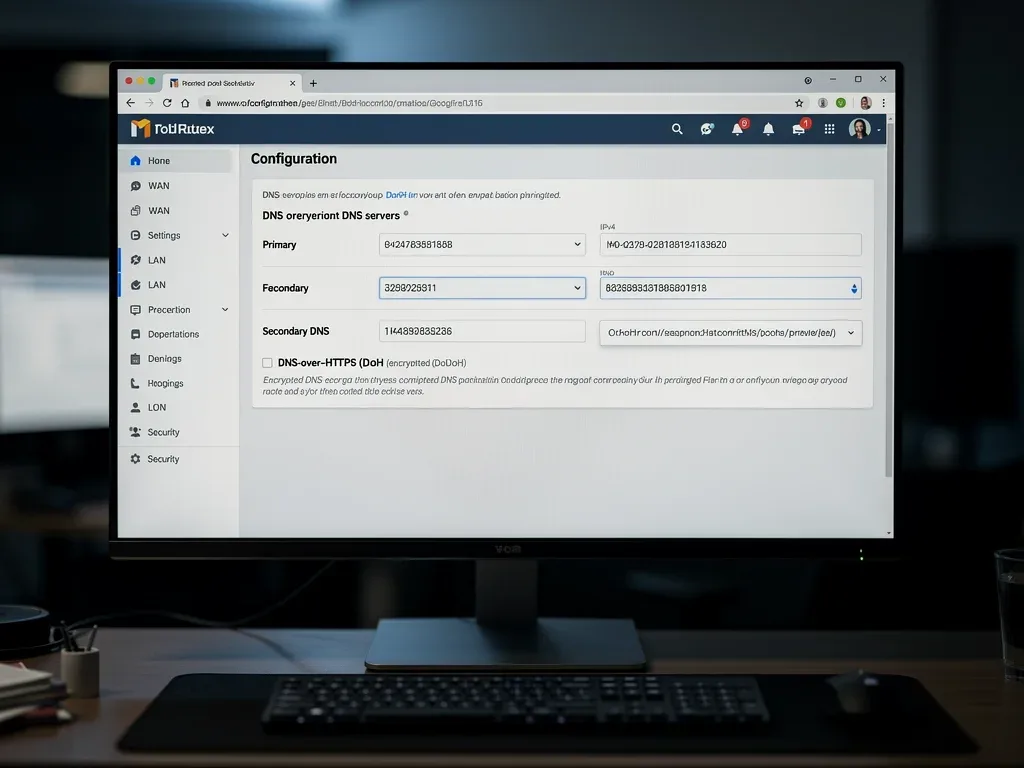
Accessing your router's administrative interface is the first critical step. This is typically done through a web browser by entering your router's default gateway IP address, often found on a sticker on the router itself.
Once logged in, navigate to the DNS settings section. The exact path may vary depending on your router's make and model, but it is usually found under 'WAN', 'Internet', 'Network', or 'Advanced Settings'.
Accessing Your Router's Administration Panel
Open a web browser and type your router's IP address (e.g., 192.168.1.1 or 192.168.0.1) into the address bar. Enter your username and password when prompted. If you haven't changed them, these are usually 'admin/admin' or found in your router's manual.
Locate the section related to DNS settings. This might be under 'Internet Settings', 'Network Settings', 'WAN Settings', or 'DHCP Server'. You're looking for fields where you can manually enter DNS server addresses.
Replace the existing DNS server addresses with the primary and secondary IP addresses provided by your chosen DoH service. For Cloudflare, these are typically 1.1.1.1 and 1.0.0.1. Save your changes and reboot your router for the settings to take effect.
Configuring DoH on Individual Devices for Enhanced Privacy
While router-level configuration offers broad protection, some devices or specific applications might require individual DoH setup for optimal privacy. This section of the DNS-over-HTTPS setup guide addresses those specific scenarios.
Certain operating systems and browsers have built-in DoH support, allowing for an even more granular control over your DNS queries. Implementing these device-specific settings can provide an additional layer of privacy and security.
This method is particularly useful for devices that frequently connect to different networks, ensuring your DNS queries remain encrypted even when away from your home router. It also serves as a fallback if your router does not support DoH directly.
Windows 10/11 DoH Configuration
Access Network Settings: Go to 'Settings' > 'Network & Internet' > 'Status' > 'Change adapter options'.
Edit Adapter Properties: Right-click on your active network adapter (Wi-Fi or Ethernet), select 'Properties', then 'Internet Protocol Version 4 (TCP/IPv4)', and click 'Properties'.
Set DoH: Choose 'Use the following DNS server addresses' and enter your preferred DoH provider's IPs. For Windows 11, you can also enable 'Encrypted DNS (DNS over HTTPS)' directly in advanced DNS settings.
macOS DoH Configuration
System Preferences: Open 'System Preferences' > 'Network', select your active connection, and click 'Advanced'.
DNS Tab: Go to the 'DNS' tab, remove any existing DNS servers, and add your chosen DoH provider's IP addresses.
Apply Changes: Click 'OK' and then 'Apply' to save the settings.
Mobile Device DoH Configuration (Android/iOS)
Android: Go to 'Settings' > 'Network & internet' > 'Private DNS'. Select 'Private DNS provider hostname' and enter the hostname of your DoH provider (e.g., 'cloudflare-dns.com' for Cloudflare).
iOS: While iOS doesn't have native system-wide DoH settings, many third-party apps (like Cloudflare's 1.1.1.1 app) can implement DoH for you, or you can use configuration profiles.
Verifying Your DNS-over-HTTPS Setup Guide Implementation
After completing the DNS-over-HTTPS setup guide, it is essential to verify that your configurations are working correctly. This step ensures that your DNS queries are indeed being encrypted and routed through your chosen DoH provider, effectively blocking ISP tracking.
Several online tools and simple command-line tests can confirm the successful implementation of DoH. This verification process provides peace of mind and confirms that your efforts to enhance privacy have been fruitful.
Without proper verification, you might unknowingly be operating under the old, unencrypted DNS system, leaving your browsing data exposed. A quick check can confirm your privacy settings are active.
Using Online DoH Test Tools
Many DoH providers offer dedicated websites to test your current DNS configuration. For example, Cloudflare provides a test page at https://1.1.1.1/help that clearly indicates whether you are using DNS over HTTPS.
These tools typically display your current DNS resolver and confirm if encryption is active. A green checkmark or a positive message usually signifies a successful DoH implementation.
If the test indicates that DoH is not active, revisit your router or device settings to ensure all steps in the DNS-over-HTTPS setup guide were followed correctly. Pay close attention to saving changes and restarting devices where necessary.
Command-Line Verification (Windows/macOS/Linux)
Windows: Open Command Prompt and type
nslookup example.com resolver_ip(replaceresolver_ipwith your DoH provider's IP, e.g., 1.1.1.1). The output should show the IP address resolved by your chosen DoH server.macOS/Linux: Open Terminal and use the
digcommand:dig @resolver_ip example.com. Similar tonslookup, this will show the DNS resolution via your specified server.
Troubleshooting Common DNS-over-HTTPS Setup Issues
Even with a clear DNS-over-HTTPS setup guide, users might encounter minor issues during implementation. Addressing these common problems efficiently ensures a seamless transition to a more private internet experience.
Problems can range from connectivity issues to the DoH settings not taking effect as expected. Understanding the typical culprits can significantly speed up the troubleshooting process.
It's important to approach troubleshooting systematically, starting with the most common and simplest solutions before moving to more complex diagnostics. Patience and careful review of each step are key.
Connectivity Problems After DoH Setup
If you experience internet connectivity issues after configuring DoH, the first step is to revert your DNS settings to automatic (or your ISP's default DNS) to confirm if DoH is the cause. If connectivity returns, the issue lies within your DoH configuration.
Double-check the IP addresses or hostnames you entered for your DoH provider. A single typo can prevent DNS resolution. Also, ensure your router or device has been properly restarted after applying the changes.
Sometimes, firewalls or security software might interfere with DoH traffic. Temporarily disabling them (with caution) can help identify if they are the source of the problem. Consult your DoH provider's support pages for specific recommendations.
DoH Not Activating Despite Configuration
Router Compatibility: Not all routers fully support DoH, especially older models. Ensure your router's firmware is up-to-date, or consider configuring DoH on individual devices instead.
Conflicting Settings: If you've configured DoH on both your router and individual devices, ensure there are no conflicts. Prioritize router settings for whole-home coverage.
ISP Interference: While rare, some ISPs might attempt to intercept or redirect DNS traffic. Using a VPN in conjunction with DoH can provide an additional layer of protection against such practices.
The Broader Impact of Your DNS-over-HTTPS Setup Guide
Implementing a DNS-over-HTTPS setup guide extends beyond personal privacy; it contributes to a larger movement towards a more secure and private internet. Your actions collectively bolster the adoption of privacy-enhancing technologies.
By encrypting your DNS queries, you not only protect your own data but also make it harder for mass surveillance programs to collect information indiscriminately. This shift creates a more resilient and privacy-respecting digital ecosystem.
This proactive step fosters a greater understanding of internet privacy among users, encouraging more individuals to take control of their online presence. It represents a significant stride towards a future where digital interactions are inherently more secure.
Contributing to a More Private Internet
Increased Adoption: Your use of DoH encourages more widespread adoption, pushing ISPs and content providers to embrace better privacy standards.
Data Minimization: By reducing the data available to ISPs, you contribute to the principle of data minimization, a cornerstone of modern privacy frameworks.
Educating Others: Sharing your experience with the DNS-over-HTTPS setup guide can empower friends and family to enhance their own digital privacy.
Key Aspect | Brief Description |
|---|---|
Privacy Enhancement | Encrypts DNS queries to block ISP tracking of browsing history. |
Setup Time | Can be completed across all home devices in under 10 minutes. |
Device Coverage | Protects all devices connected to the home network via router configuration. |
Key Benefit | Significantly reduces data ISPs can collect, enhancing online security. |
Frequently Asked Questions About DNS-over-HTTPS
What exactly is DNS-over-HTTPS (DoH)?▼
DNS-over-HTTPS (DoH) is an internet protocol that encrypts Domain Name System (DNS) queries using HTTPS. This prevents third parties, including your ISP, from seeing which websites you visit. It's a crucial step in enhancing online privacy and security by making your DNS traffic private.
How does DoH help block ISP tracking?▼
By encrypting your DNS queries, DoH prevents your ISP from seeing the specific domain names you are trying to resolve. Without this information, ISPs cannot compile a detailed browsing history of your activities, significantly reducing their ability to track your online behavior and sell your data.
Is it complicated to set up DoH on all my home devices?▼
No, implementing a DNS-over-HTTPS setup guide is surprisingly straightforward. By configuring DoH on your home router, you can secure all connected devices simultaneously. For individual devices, many operating systems and browsers now offer native DoH support, making setup quick and easy.
Which DoH providers are recommended for home users?▼
Several reputable DoH providers offer excellent services for home users. Cloudflare (1.1.1.1) is highly regarded for its speed and strong privacy policy. Google Public DNS (8.8.8.8) is another popular and reliable choice. Quad9 (9.9.9.9) focuses on security by blocking malicious domains, providing a secure browsing experience.
Will using DoH slow down my internet connection?▼
For most users, implementing DoH will have a negligible impact on internet speed, and in some cases, it can even improve DNS resolution times. Reputable DoH providers operate globally distributed servers designed for high performance. The encryption overhead is minimal and typically unnoticeable during daily browsing.
Perspectives
The widespread adoption of a robust DNS-over-HTTPS setup guide marks a critical juncture in the ongoing battle for digital privacy.
This technological shift empowers individuals to reclaim autonomy over their browsing data, challenging traditional ISP data collection practices.
As more users implement DoH, the collective impact will push the industry towards more privacy-centric standards, fostering a healthier and more secure internet ecosystem for everyone.